MDR Cybersecurity: How Managed Detection And Response Works In Modern Networks

MDR: Detection Methods and Security Analytics
Detection methods within MDR typically span rule-based signatures, behavioural analytics, and statistical or machine-learning models. Rule-based detections identify known patterns such as specific malware signatures or suspicious command sequences, while behavioural analytics seek deviations from established baselines, such as unusual process creation rates or atypical network destination patterns. Machine-learning techniques may surface anomalies that do not match predefined rules, but they often require tuning and context to reduce false positives and align with the organisation’s normal activity patterns.
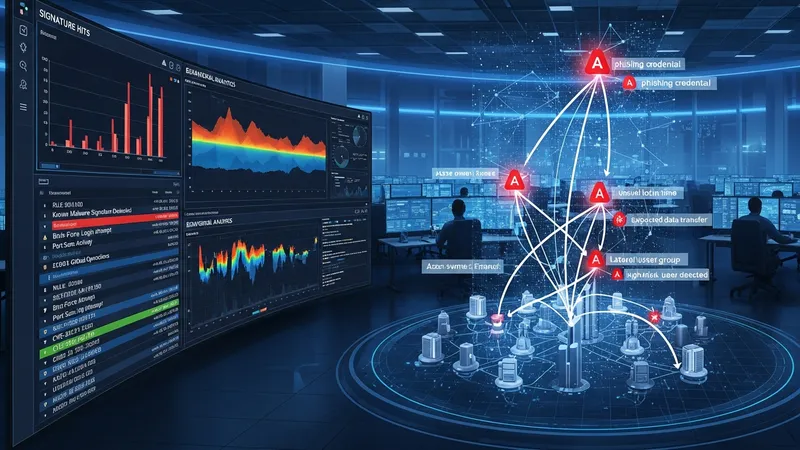
Correlation engines in SIEM or XDR systems help connect discrete alerts into coherent hypotheses about multi-stage intrusions. For example, a sequence that includes a phishing-induced credential use, followed by unusual login times and unexpected data transfers, can indicate an escalating compromise. Correlation often relies on enrichment with contextual attributes such as asset owner, business unit, and known vulnerabilities, which may help prioritise investigations based on potential impact rather than alert volume alone.
False positives and alert fatigue are practical concerns for detection operations. High volumes of low-fidelity alerts can divert analyst time from meaningful investigations. MDR approaches commonly include iterative tuning, where detections are refined based on feedback from investigations, and suppression rules are applied for known benign patterns. Additionally, analysts may maintain white-lists and contextual allowlists for scheduled processes or known maintenance activities to reduce unnecessary escalations.
Threat intelligence can augment detection by associating observed indicators with known adversary infrastructure or tactics. Intelligence may come from open-source feeds, commercial providers, or industry sharing groups, and it often helps prioritise alerts for investigation. However, reliance on external indicators requires validation because IOCs can be recycled or noisy; combining intelligence with local context tends to yield more actionable signals than standalone IOC matches.