Independent Penetration Testing: Why Third-Party Security Assessments Matter

Testing methodology and validation processes used by third parties
Structured methodologies often begin with reconnaissance to map assets and services, followed by vulnerability identification using both automated tools and manual inspection. After initial findings, assessors commonly perform risk validation through controlled exploitation or proof-of-concept actions to gauge potential impact. Validated findings typically include reproducible steps and supporting evidence. Methodologies may reference public standards or community frameworks to ensure consistency and facilitate stakeholder understanding of results.
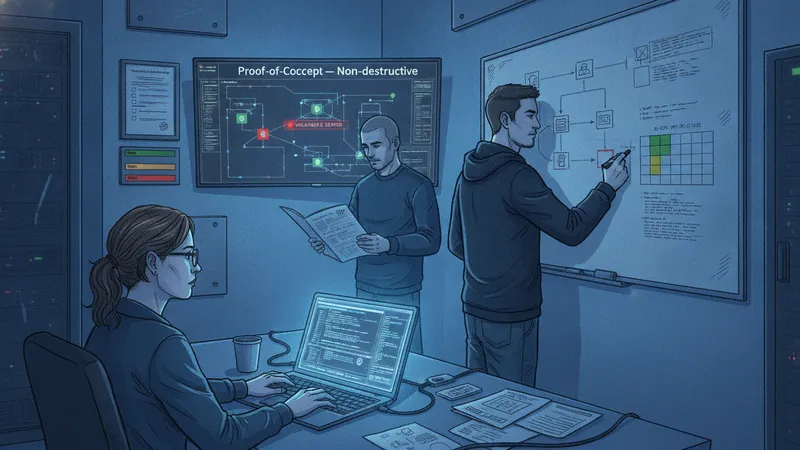
Controlled exploitation is often treated cautiously to avoid destabilising production services. Assessors may document which exploit actions are permitted and where a non-destructive verification is preferred. For example, proof-of-concept interactions may confirm that a vulnerability exists without performing destructive payloads. This approach allows organisations to prioritise remediation efforts with a clearer view of practical exploitability while managing operational risk during testing.
Credentialed testing is commonly used to reveal issues that are not visible externally, such as weak privilege separation or flawed access control logic. When credentials are provided, assessors typically validate the scope of access and note any escalations or privilege abuses observed. Testing teams may combine network-level techniques with application-focused checks to construct plausible attack paths from initial access to sensitive assets, documenting lateral movement techniques and required conditions.
Quality of findings often depends on the assessment’s depth and the assessor’s familiarity with the environment. Neutral criteria such as reproducibility, availability of exploit details, and mapping to known weaknesses help stakeholders interpret results. Independent assessors commonly include mitigation suggestions and references to public guidance so that remediation teams can align fixes with accepted practices rather than ad hoc remedies.