Independent Penetration Testing: Why Third-Party Security Assessments Matter

Application, network and cloud testing approaches within third-party assessments
Application testing frequently emphasises input validation, authentication, session management and business logic flows. Tests may map to community-driven lists of common weaknesses and include API security checks for endpoints handling structured requests. Manual inspection often supplements automated scanning to catch complex logic issues that tools may not flag. Findings commonly point to both coding defects and architectural choices that affect application resilience under adversarial conditions.
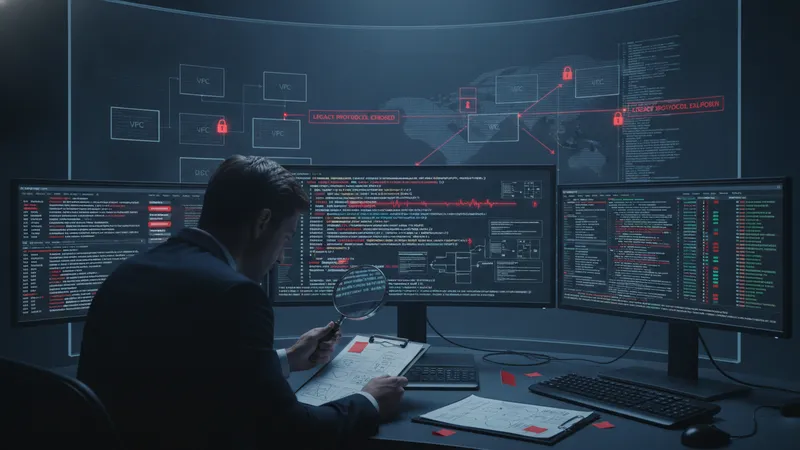
Network testing may include service enumeration, banner analysis, exposure checks for legacy protocols and verification of segmentation controls. Internal network assessments often focus on how easily an attacker could move between segments or access privileged infrastructure. Assessors typically describe the sequence of steps used to move laterally and the conditions that enabled access, providing context for prioritising segmentation or access-control improvements.
Cloud and API assessments commonly evaluate identity and access management, storage permissions, misconfigured network ACLs and exposed management interfaces. Cloud-native features such as role-based access, ephemeral credentials and managed services can change the attack surface, so assessors often examine service-specific configurations and privilege boundaries. Where possible, tests are designed to avoid disrupting production cloud services while verifying excessive permissions or publicly readable resources.
Practically, many organisations find that combining focused application reviews with periodic infrastructure and cloud checks yields a clearer picture of systemic weaknesses. Test teams may recommend defensive controls such as improved monitoring, hardened baselines and tighter privilege models, framed as considerations to reduce exploitability rather than as prescriptive directives. Continual refinement of scope and methods keeps assessments aligned with changing environments.